7 min read
Quantum-safe data center interconnect: How PQC and QKD work together in practice
Marc Könn : November 4, 2026
Contents
Connections between data centers must defend against two threats simultaneously: conventional cyberattacks and the “Harvest Now, Decrypt Later” scenario. In this scenario, cybercriminals collect encrypted data today with the aim of decrypting it later using powerful quantum computers.
At our Customer Briefing Center in Langen, near Frankfurt am Main, we explored how this threat can be addressed today. We validated different combinations of post-quantum cryptography (PQC) and quantum key distribution (QKD). The results show that the two technologies can already be combined in a hybrid approach.
In this article, I put current developments into context and explain how our findings affect the planning and operation of modern network infrastructures.
Quantum-resistant cryptography: From regulation to practice
The migration to quantum-safe encryption is becoming a concrete procurement and transformation challenge for businesses and public institutions. Regulatory momentum is also growing. In November 2024, Germany’s Federal Office for Information Security (BSI), together with 17 European partner countries, published a statement calling on businesses, critical infrastructure operators and public administrations to actively initiate the transition to post-quantum cryptography (PQC). The question is no longer whether quantum-resistant methods are needed, but how to introduce them quickly and systematically.
Germany’s Federal Financial Supervisory Authority, BaFin, also emphasizes the need for action. It supports the G7 Cyber Expert Group’s roadmap for PQC migration and recommends that financial institutions prepare now for risks such as “Harvest Now, Decrypt Later.” As guidance, the roadmap calls for critical systems to be migrated by 2030 where possible, and other systems by 2035.
This regulatory pressure coincides with a level of technical maturity that would have sounded like science fiction just a few years ago. In August 2024, the US National Institute of Standards and Technology (NIST) published its first finalized standard for a quantum-resistant key encapsulation mechanism, standardizing ML-KEM as FIPS 203. Source: NIST CSRC: FIPS 203 final.
At the same time, quantum key distribution (QKD) products and standardized interfaces are creating opportunities to combine the two technologies in hybrid architectures. Whether such a combination is suitable for production use depends on the infrastructure, security requirements and specific implementation.
The financial sector, in particular, is increasingly taking a proactive stance.
In the Quantum Safe Financial Forum (QSFF), initiated by Europol, leading institutions such as Allianz, Barclays, BNP Paribas, Santander and other European banks are working together on strategies for migrating to quantum-safe encryption. The forum advocates a coordinated and timely transition to PQC to protect sensitive financial data over the long term.
Central banks are also driving progress. In Project Leap, Deutsche Bundesbank, Banque de France and the Bank for International Settlements (BIS) tested the use of quantum-safe cryptography in payment systems. The results of these pilot projects show that migration is technically feasible and should already be planned to safeguard the long-term resilience of critical financial infrastructures. Source: BIS: Project Leap.
For regulators, central banks, insurers and financial institutions, the transition to PQC is not a long-term research question but a strategic necessity. Regulatory pressure, standardized methods and successful pilot projects demonstrate that the transition to quantum-safe communication is already well underway. Post-quantum cryptography should be regarded as a standard for protecting data.
The threat: “Harvest Now, Decrypt Later”
A key risk to long-term data security is the “Harvest Now, Decrypt Later” (HNDL) scenario. Attackers are already intercepting and storing encrypted data streams with the aim of decrypting them later using cryptographically relevant quantum computers.
This is not a hypothetical risk but a development happening today: long retention periods for personal, strategic or security-sensitive data extend the time during which data intercepted today must remain secure—even decades from now.
Leading security authorities, including NIST, the NSA, CISA, the UK’s NCSC and Germany’s BSI, explicitly highlight this risk. They warn that attackers could already be collecting and storing encrypted data that requires long-term protection, intending to decrypt it once cryptographically relevant quantum computers become available.
Post-quantum cryptography: The mathematical layer of protection
Post-quantum cryptography (PQC) refers to cryptographic methods whose security is based on mathematical problems that, according to current knowledge, cannot be efficiently solved by either classical computers or future quantum computers. Unlike widely used methods such as RSA or elliptic curve cryptography (ECC), whose security relies on the difficulty of prime factorization and the discrete logarithm problem, respectively, PQC uses new classes of mathematical problems.
The reason for this shift is that a sufficiently powerful quantum computer running Shor’s algorithm would fundamentally threaten the security of many public-key methods in use today. New cryptographic methods have therefore been developed to provide a high level of security even in the age of quantum computing. In August 2024, the National Institute of Standards and Technology (NIST) published the first three finalized PQC standards as FIPS 203, FIPS 204 and FIPS 205. Source: NIST: First 3 Finalized Post-Quantum Encryption Standards.
FIPS 203 is particularly relevant for securing data connections between data centers. ML-KEM enables the secure exchange of symmetric session keys between two endpoints. The standardization process is complete, meaning ML-KEM can be implemented in hardware and software products and deployed in production environments.
PQC is, however, just one component of a comprehensive quantum-safe security architecture. The BSI and the NSA consider post-quantum cryptography a foundational pillar, but emphasize that these methods, like classical cryptographic methods, must continue to be evaluated and tested—even after years of public analysis. Sources: BSI: Quantum technologies and quantum-safe cryptography; NSA: Post-Quantum Cybersecurity Resources.
Quantum key distribution complements PQC at the key distribution level, further strengthening the security of the communication link.
Quantum key distribution: The physical layer
Quantum key distribution (QKD) uses the quantum-mechanical properties of photons to generate and distribute symmetric keys between two endpoints. Attempts to intercept the quantum link can cause measurable changes and can therefore be detected. QKD adds a physical layer of protection to the mathematical security of cryptographic methods.
The European Telecommunications Standards Institute (ETSI) has defined a standardized, REST-based interface for key delivery, for example in ETSI GS QKD 014. Applications can use it to obtain keys from a QKD network independently of the protocol used. This provides a foundation for connecting encryption solutions from different vendors to the same QKD infrastructure.
QKD does not replace post-quantum cryptography, but can complement it in suitable scenarios. Both the BSI and the NSA recommend evaluating the two approaches accordingly. QKD is intended as a complement to PQC in a hybrid approach, not as a replacement. PQC forms the foundational pillar, while QKD offers additional value where a physical basis of trust strengthens the security of the communication link.
Connecting data centers over fiber-optic links provides suitable conditions for QKD. Connections between sites can be carefully planned and controlled. Distances often fall within metropolitan ranges, keeping the chain of trust required for key generation manageable.
In the face of the “Harvest Now, Decrypt Later” (HNDL) threat, the focus is on the long-term protection of confidential data. An attempt to intercept the quantum link changes the quantum state. This can leave measurable traces, making it more difficult to obtain keys undetected and use them later for decryption. ML-KEM complements this physical layer of protection with a standardized mathematical mechanism for key exchange. Combining QKD and PQC reduces reliance on any single security assumption and provides a foundation for quantum-safe communication links.
The validation: Adtran FSP 3000 with S-Flex and software version 8.1.1
At our Customer Briefing Center, we successfully validated the integration of QKD keys into an optical transmission system based on the Adtran FSP 3000C. We combined quantum key distribution (QKD) with post-quantum cryptography (PQC) using the standardized ML-KEM mechanism. dacoso was the first company in this field to test and implement this combination in such a system. With software version 8.1.1, the interfaces required to connect to QKD key sources are fully integrated into the FSP 3000C platform and the S-Flex module.
The S-Flex module is a versatile FSP 3000 muxponder card for modern data center interconnect (DCI) applications. With a total capacity of 400 Gbit/s, it supports a range of applications and services, including Ethernet, Fibre Channel, CELR and RoCE (IBM Z/mainframe), as well as OTN services.
To protect payload data, the module uses low-latency, AES-256-based Layer 1 encryption. The required session keys are established using quantum-resistant key exchange based on ML-KEM (post-quantum cryptography, PQC). External key material can also be incorporated. A hybrid key derivation function (KDF) combines PQC-based and externally supplied key material—for example, from QKD systems—to create a particularly robust security approach.
The S-Flex card offers a high degree of cryptographic agility, increasing resilience against future cryptographic threats, including potential attacks by quantum computers. It also supports the implementation of regulatory requirements for quantum-resistant communication infrastructures in critical infrastructure, government, financial and enterprise networks.
For more information, see the Adtran FSP 3000 S-Flex data sheet.
Interoperability and practical suitability
Our test scenario is designed to bring different systems together: multiple QKD systems can be connected in parallel, with keys delivered through standardized interfaces. The optical transmission platform can be configured independently of any particular vendor. This keeps the architecture flexible and reduces dependence on individual suppliers.
For data center operators, this approach offers a gradual and cost-effective path to quantum-safe data communication. Existing fiber-optic infrastructure can remain in use rather than being completely replaced. Modernization focuses specifically on the encryption layers: new cryptographic methods can be integrated into muxponders, while QKD components can be added on a modular basis.
At our Customer Briefing Center in Langen, you can experience the solution in operation under realistic conditions. The live demonstration shows the entire chain—from key generation and automated key delivery to the encryption of optical data streams at speeds of up to 400 Gbit/s across various fiber-optic links.
This practical perspective is essential. While laboratory environments provide valuable technical insights, they can only partially reflect the integration, availability and latency requirements of production networks. A live demonstration provides a sound basis for decisions about planning and implementing quantum-safe data center interconnects.
“In our view, combining post-quantum cryptography and quantum key distribution is the most sustainable way to protect data in transit, even when that data needs to remain secure over long retention periods. At our demo center, we show that this combination works today, is interoperable and can be integrated into existing transmission links.”
Felix Pohl, CEO at dacoso
Conclusion: Quantum-safe encryption starts with concrete risk management
FIPS 203 provides a standardized, quantum-resistant key encapsulation mechanism. ETSI GS QKD 014 defines the interface through which applications can obtain quantum-generated keys from QKD networks. Combining PQC and QKD offers an approach to meeting current requirements for secure data communication and addressing the “Harvest Now, Decrypt Later” (HNDL) risk—particularly for data that must be protected and retained over long periods.
Our validation in Langen shows that this architecture can be implemented on a commercially available optical platform and that interoperability between different vendors works in practice. For IT and security leaders, this raises concrete questions about the next steps:
- Which existing connections can already be secured against quantum threats?
- Which migration steps can be implemented in the short term?
- Which data flows are most vulnerable to HNDL and should be protected first?
If you would like to explore these questions using a realistic setup, we warmly invite you to our Customer Briefing Center in Langen. Experience PQC and QKD working together in a live environment and discuss with us which next steps make sense for your infrastructure.
Marc Könn, Product Manager Solutions, dacoso
Headline
Add content here.
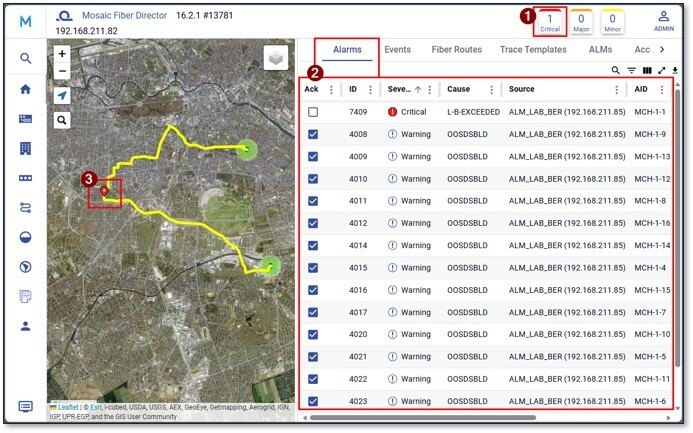
An excavator. For example... Immediately detect and resolve incidents on the fiber-optic line using ALM
What happens on a fibre-optic link – for example, between two data centres – often goes unnoticed for a long time. Yet even minor changes can lead to...